

The Ultimate Guide to Application Security
A curated Asian edition of IndustrialDay news, analysis, interviews, reviews, job moves, and related resources for Application Security.
What to know about Application Security
Application Security focuses on protecting software applications from vulnerabilities and cyber threats throughout their development and operational life cycles. This critical field addresses challenges such as runtime protection, secure coding practices, DevSecOps integration, API security, cloud-native environments, and mitigating attacks like DDoS, supply chain risks, and malicious bot traffic.
Exploring the latest stories in Application Security reveals how advancements like AI and automation are enhancing threat detection, vulnerability management, and developer workflows, while highlighting ongoing risks found in mobile apps, open source components, and cloud deployments. Readers can gain insights into best practices, emerging technologies, and strategies to safeguard applications against evolving cyber threats.
Whether you’re a developer, security professional, or business leader, staying informed about Application Security developments helps in building resilient software, maintaining compliance, and protecting user data in an increasingly complex digital landscape.
Asian Application Security News
Regional stories with direct local relevance
Broadcom launches VMware Private AI Cloud for enterprises
Enterprises can now keep AI workloads and sensitive data on the same private cloud, as Broadcom adds governance and security controls.
Why penetration testing must move at the speed of attackers
Stolen credentials can become an operational foothold within hours, leaving annual assessments too slow to catch the real attack paths.

Broadcom adds AI security tools to VMware private cloud
Private cloud operators may cut hardware costs by a third as Broadcom folds AI-assisted threat prevention and API security into VMware tools.
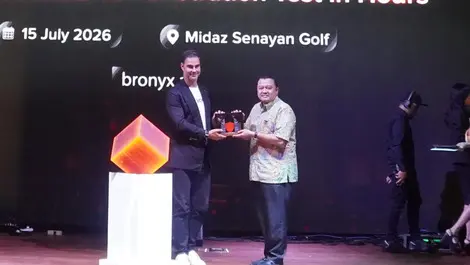
ITSEC Asia launches Bronyx AI for automated testing
Businesses may get security test results in hours as ITSEC Asia's new platform flags risks and keeps human consultants in the loop.
Agoda launches public bug bounty with USD $6,000 reward
Researchers can now earn up to USD $6,000 for exposing flaws in Agoda's core web services, APIs and mobile app via HackerOne.

A10 Networks buys TrojAI to boost AI security tools
The deal gives customers red teaming and runtime protection for AI systems as enterprises rush to secure models and autonomous agents.
Analyst Insights
Research and market analysis connected to Application Security
Netskope launches control to block risky AI agent actions
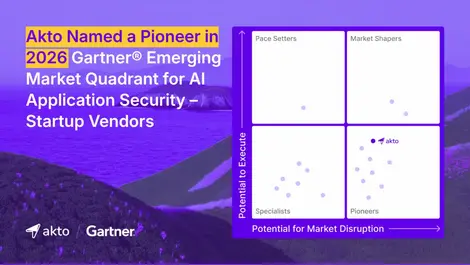
Akto named pioneer in Gartner's AI security quadrant
F5 named Market Shaper in Gartner AI security quadrant
RevEng.AI launches binary analysis models for code
Survey finds AI access controls lag behind confidence
Expert Columns
AI closes vulnerability window as zero-day exploits surge
Why penetration testing must move at the speed of attackers
When AI memory, simulation and provenance collide
Supercharged security: Cyber risk in the age of frontier AI
Buying more tools won't scale your security ambitions, operational maturity will
A strategic blueprint for governing AI-enabled software development

Why ERP is not just another platform you can rebuild with AI code
As agentic development accelerates, workflow auditability becomes a bottleneck
Why organisations in Asia Pacific are rethinking their AI deployment strategies
Leading Agentic AI teams in Singapore: What technology leaders should know
Interviews
Interviews and video coverage from the network

Recent Application Security News
Fastly launches AI controls as machine traffic surges
Machine-generated requests now account for more than half of Fastly's network traffic, intensifying pressure to govern AI costs and security.
StackHawk launches Wingman to fix flaws in AI coding
Security teams may cut backlogs as Wingman finds, fixes and verifies flaws inside AI coding tools before pull requests are opened.
Azul launches AI assistant for Java security checks
IT teams can now spot unpatched Java versions and Oracle licensing exposure in live production data, cutting the risk of audit surprises.
Palo Alto launches continuous AI defence for clients
Attackers are exploiting AI faster than many defences can respond, prompting a shift to continuous testing for hidden exposures.
Akamai warns of blind spots in workplace agentic AI
More than 40% of enterprise users have installed AI browser tools, leaving security teams struggling to spot permission changes and rogue agents.
A10 launches AI Gateway for enterprise model control
Enterprises could get tighter control over AI spend and access as A10's gateway routes requests, tracks usage and enforces policy.
Fastly launches AI firewall & runtime control tools
Machine-generated traffic is driving up costs and security risks as Fastly adds controls for AI systems now moving into production.
Delinea joins Anthropic project to test identity security
It could expose faults in software that governs access to sensitive systems, with no customer data included in the AI-led testing.
Mandiant warns of AI agents fuelling new attack risks
Autonomous systems are now creating fresh avenues for code theft, remote execution and runaway cloud spending, Mandiant says.
Tanium tests Anthropic AI for code vulnerabilities
By probing its own production code, Tanium is aiming to catch flaws before attackers can exploit software used by thousands of organisations.
CrowdStrike links PhantomRaven malware to bug bounty hunter
The stealer's use of typosquatted npm packages has raised fears that bug bounty channels are being abused to monetise stolen developer data.
Secure Code Warrior launches Citizen AI training programme
With most firms using AI in daily work but few staff ready for it, the programme targets non-developers handling sensitive data and automations.
Rubrik launches Code Guardian & expands Anthropic ties
The private previews aim to help security teams spot exploitable code chains and connect AI agents to Rubrik's governance tools more safely.
AWS adds OpenAI's GPT-6 Astra to Bedrock for business
Businesses can now run OpenAI's latest frontier model on AWS without managing infrastructure, as Bedrock gains access to GPT-6 Astra.

F5 launches AI security to monitor worker tool use
As staff hand more tasks to AI agents, firms need audit trails and policy controls to stop unauthorised access and risky data moves.
Google warns cyber attackers are moving to agentic AI
Attackers are compressing intrusions into hours, leaving defenders less time to spot and stop credential-harvesting campaigns.
Checkmarx joins Anthropic's Project Glasswing on defence
The collaboration could help security teams spot flaws before attackers exploit them, as exploitations increasingly happen on or before disclosure.
HP patches three high-severity flaws in Easy Start
Mac users face a higher risk of tampered printer installs after HP fixed three bugs in Easy Start, including a root-level file flaw.
A-LIGN buys Pathfynder in cyber services expansion
The deal gives A-LIGN customers direct access to penetration testing and red teaming as firms seek fewer vendors for cyber compliance and defence.
Reco launches Browser Guard to curb shadow AI risks
Security teams can now block employees' unsanctioned AI use in browsers before prompts or agent actions expose sensitive data.